Free Cors Header Generator Online
Quickly generate CORS headers for APIs and web apps. The 2026 CORS Header Generator ensures secure cross‑origin requests, faster setup, and improved compatibility.
100% private — generation runs in your browser. Never reflects Origin blindly; wildcard cannot combine with credentials.
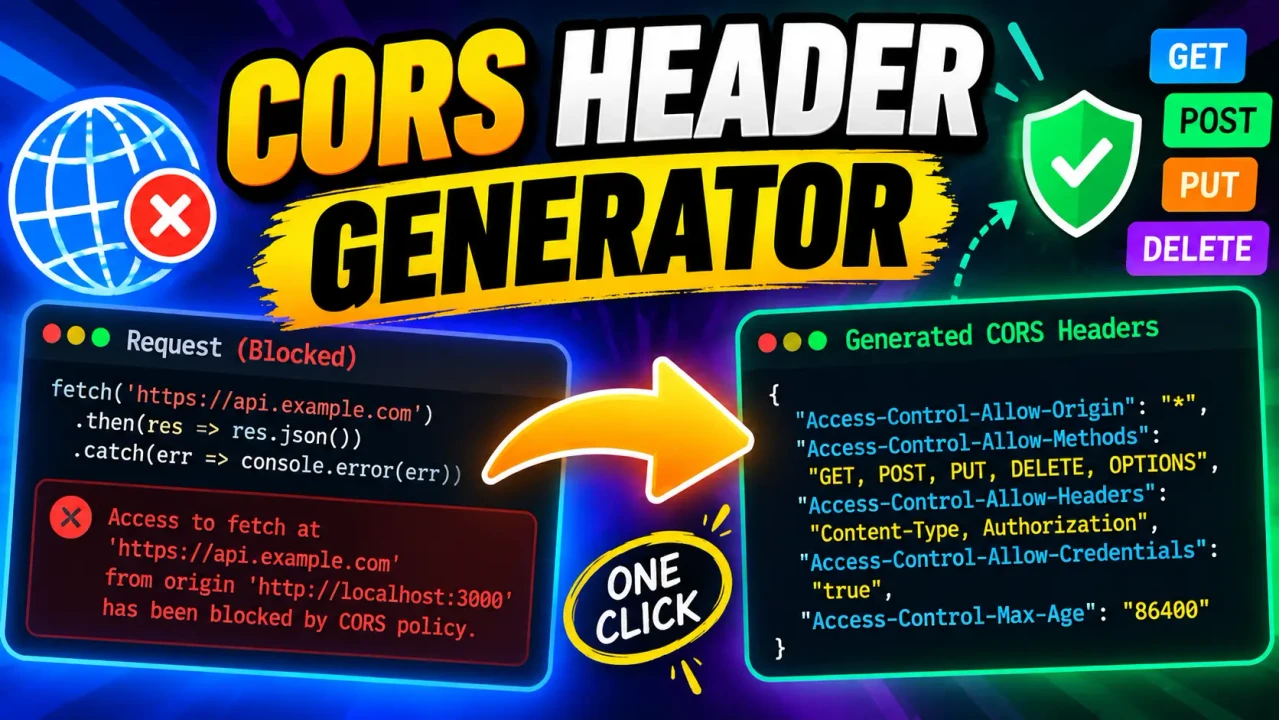
CORS Header Generator
TL;DR Summary
CORS Header Generator helps you create HTTP Cross-Origin Resource Sharing (CORS) header configuration for a web server or API. Use the generated headers as a configuration starting point, and avoid entering sensitive information because the supplied tool context does not document how entered data is processed or stored.
About This Tool
CORS Header Generator is a developer tool for creating CORS response-header configuration. CORS, or Cross-Origin Resource Sharing, controls whether a browser allows a web page from one origin to request resources from another origin.
This is useful when a frontend and backend use different origins. For example, a web application might run on one origin while its API runs on another. A browser can block a cross-origin request when the server does not return the appropriate CORS headers. The CORS Header Generator provides a practical way to prepare the header values needed for this type of configuration.
The main users of this tool are web developers, API developers, frontend developers, backend developers, DevOps users, and people configuring web servers. It can also help when troubleshooting browser messages related to CORS policy, especially when an API works directly but a browser application cannot access its response.
What CORS Headers Do
CORS headers are HTTP response headers. They tell a browser what cross-origin requests a server is willing to accept. Common CORS headers include Access-Control-Allow-Origin, Access-Control-Allow-Methods, Access-Control-Allow-Headers, Access-Control-Allow-Credentials, Access-Control-Expose-Headers, and Access-Control-Max-Age.
The exact headers needed depend on the request and the server's policy. A simple cross-origin request may require fewer settings than a request that uses custom headers, non-simple HTTP methods, or credentials.
Inputs
The available input fields and options depend on the implementation of the CORS Header Generator. The supplied tool context identifies the utility by name but does not document its exact form fields or selectable options. Therefore, users should follow the labels shown in the tool rather than assuming that every possible CORS header is available.
Typical CORS configuration can involve an allowed origin, permitted HTTP methods, permitted request headers, credential support, exposed response headers, and browser cache duration for preflight results. These settings should only be configured when they are actually offered by the tool.
Outputs
The expected output of a CORS Header Generator is HTTP header configuration that can be used as a reference when configuring an API or web server. Depending on the page implementation, the result may be displayed as header lines or configuration text that can be copied into a server configuration.
A typical header has a name and a value. For example:
Access-Control-Allow-Origin: https://example.comThis example illustrates the format of a CORS response header. It is not a claim about the exact output format of this Toolhox implementation.
How to Use
- Step 1: Open the CORS Header Generator and review the available configuration fields.
- Step 2: Enter or select the cross-origin settings required by your application, such as the allowed origin, methods, or headers when those options are provided.
- Step 3: Review the generated CORS header values before using them on your server or API.
- Step 4: Copy the generated configuration into the appropriate server, API gateway, framework, or reverse-proxy configuration.
- Step 5: Test the browser request against the configured endpoint and confirm that the returned response contains the expected CORS headers.
Technical Explanation
CORS does not use a single mathematical formula. It is an HTTP policy mechanism. The browser sends a request with an Origin header when a cross-origin request requires CORS handling. The server then returns response headers that describe whether that origin and request are allowed.
The central relationship can be described as:
Browser origin
        ↓
HTTP request with Origin
        ↓
Server CORS policy
        ↓
CORS response headers
        ↓
Browser allows or blocks access
For example, an API may return:
Access-Control-Allow-Origin: https://app.example.comThis tells the browser that the specified origin is allowed to access the resource under the CORS policy represented by that response.
For requests that require a preflight check, the browser can first send an OPTIONS request. The server can respond with headers such as:
Access-Control-Allow-Origin: https://app.example.com
Access-Control-Allow-Methods: GET, POST
Access-Control-Allow-Headers: Content-Type, Authorization
The browser uses this response to determine whether the intended cross-origin request is permitted.
Important CORS Options
| Header | Purpose |
|---|---|
Access-Control-Allow-Origin |
Specifies which origin can access the resource. |
Access-Control-Allow-Methods |
Specifies HTTP methods permitted by the CORS policy. |
Access-Control-Allow-Headers |
Specifies request headers that the server permits for cross-origin requests. |
Access-Control-Allow-Credentials |
Controls whether credentials can be included in supported cross-origin requests. |
Access-Control-Expose-Headers |
Specifies response headers that browser-side code may access. |
Access-Control-Max-Age |
Controls how long a browser may cache applicable preflight information. |
Not every application needs every header. The appropriate configuration depends on how the frontend communicates with the server.
Preset Examples / Quick Reference
A basic origin-specific CORS response can look like this:
Access-Control-Allow-Origin: https://app.example.comA policy that also permits common methods might look like:
Access-Control-Allow-Origin: https://app.example.com
Access-Control-Allow-Methods: GET, POST, OPTIONS
A policy for requests that send selected custom headers may also include:
Access-Control-Allow-Headers: Content-Type, AuthorizationThese examples demonstrate standard CORS header syntax. They are examples of configuration patterns, not a statement that these exact values are built into the Toolhox generator.
Why Use This CORS Header Generator & How Our CORS Header Generator Beats the Competition
| Method | Ease of Use | Calculation Speed | Best For | Limitations |
|---|---|---|---|---|
| Toolhox CORS Header Generator | Uses a dedicated CORS header generation workflow | Designed to generate configuration from the supplied inputs | Preparing CORS header configuration | The exact available options and generated configuration depend on the tool implementation. |
| Manual Configuration | Requires knowledge of CORS headers | Depends on the user | Developers who already know the required policy | It is easier to omit or mistype a required header. |
| Spreadsheet | Requires a custom setup | Depends on the spreadsheet design | Documenting or comparing configuration values | Not naturally designed for HTTP header generation. |
| Professional Development Tools | Can require broader technical knowledge | Depends on the tool and workflow | Complex application development and debugging | May provide many features beyond a focused CORS configuration task. |
The practical value of a dedicated CORS Header Generator is that it focuses the task on CORS response-header configuration instead of requiring users to construct every header manually. However, generated headers still need to match the application's actual security and access requirements.
Assumptions and Limitations
CORS configuration is controlled by browser rules and server responses. Generating a header does not automatically change the server. The generated values must be placed in the correct server, framework, API gateway, or proxy configuration before they affect requests.
A CORS policy should be specific to the application's requirements. Allowing an origin, method, or request header that the application does not need can create an unnecessarily broad access policy. Credentials also require careful configuration because credentialed cross-origin requests have additional browser rules.
The supplied tool context does not document the CORS Header Generator's exact internal implementation, complete input list, server-side processing behavior, storage policy, or validation rules. For that reason, this page does not claim that entered data is processed locally, uploaded, stored, or automatically validated.
Users should also remember that CORS is a browser access-control mechanism. It is not a replacement for authentication, authorization, access controls, input validation, or other server-side security controls. A generated CORS policy should not be treated as a complete security configuration.
For production systems, review the resulting headers against the application's actual frontend origins, API routes, HTTP methods, request headers, credentials requirements, and deployment architecture. If the API handles sensitive information or supports a security-sensitive application, appropriate technical review may be needed before changing the production CORS policy.