Htaccess Password Protection Generator
Easily secure your website directories with our free .htaccess password protection generator. Create safe .htpasswd files in seconds.
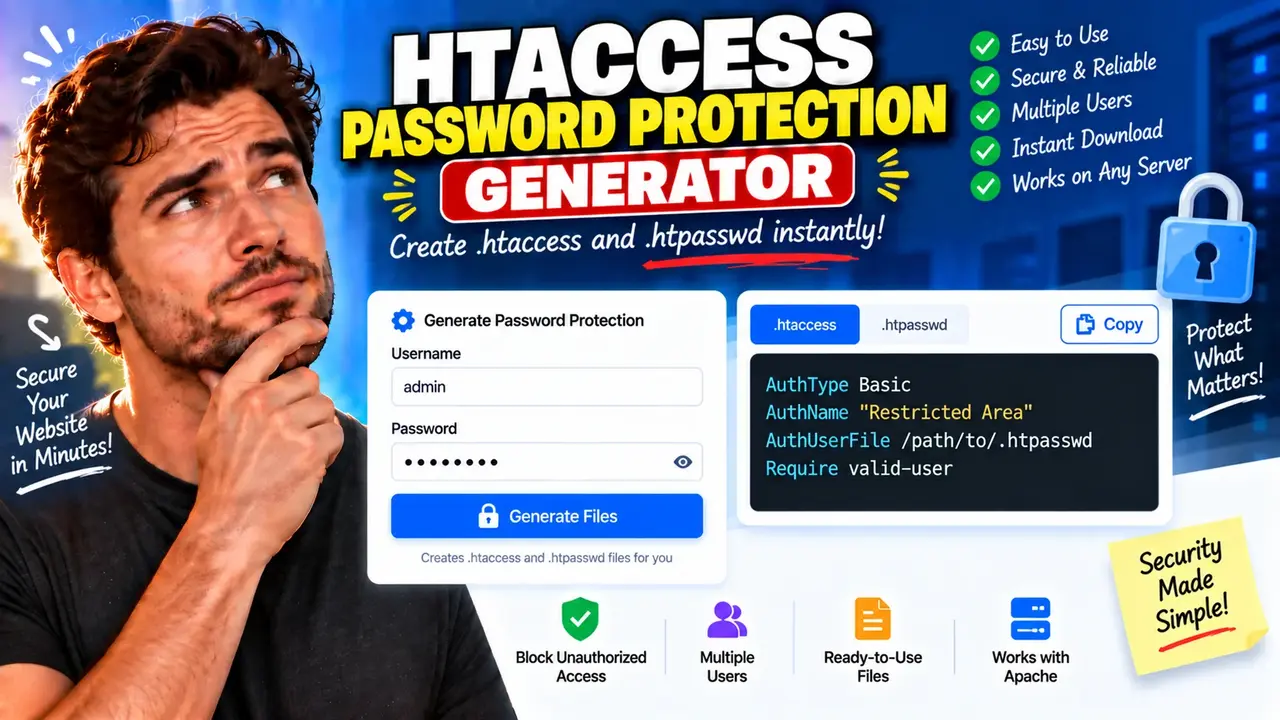
HTACCESS Password Protection Generator
TL;DR Summary
The HTACCESS Password Protection Generator is a web-based utility intended to help create Apache .htaccess password-protection configuration text. The supplied tool information does not document its exact input fields, processing method, or storage behavior, so treat the generated configuration as a starting point and avoid entering sensitive information unless the page clearly explains how that information is handled.
What Is the HTACCESS Password Protection Generator?
The HTACCESS Password Protection Generator is designed for users who need to create password-protection rules for an Apache-powered website. An .htaccess file is a configuration file commonly used on Apache web servers to control access to a directory or apply server-level rules without changing the main server configuration.
Password protection can be useful when a website owner wants to restrict access to a directory, staging area, development page, private section, or other web content. Instead of manually assembling Apache authentication directives, a generator can provide configuration text in a format that can be reviewed and placed into the appropriate configuration file.
This tool is relevant to website owners, developers, system administrators, web designers, and other users who work with Apache hosting. It can also be useful when someone understands the goal of protecting a directory but does not want to build the required configuration syntax entirely from memory.
What Does the Tool Generate?
The stated purpose of this tool is to generate .htaccess password-protection configuration. The exact output fields and configuration options are not documented in the supplied tool context, so this page does not assume a particular username field, password field, authentication realm, directory path, or other option unless the live tool provides it.
The expected result is configuration text intended for use with Apache's .htaccess mechanism. Because server configuration can vary between hosting providers and Apache environments, generated text should be reviewed before it is used on a live website.
Who Can Use It?
The generator is intended for people working with websites hosted on Apache or an environment that supports the relevant .htaccess configuration method. It may be useful for:
- Website owners protecting non-public website areas.
- Developers setting up restricted development or staging directories.
- Web designers managing access to temporary project areas.
- Administrators working with Apache-based hosting.
- Users who need a starting point for an Apache password-protection configuration.
The tool is not a replacement for understanding the server environment. Before applying an access-control configuration, confirm that the hosting account supports .htaccess files and the authentication directives required by the generated configuration.
Inputs and Options
The supplied information identifies the tool as a password-protection generator but does not provide a verified list of its interface fields. For that reason, the exact required and optional inputs should be taken from the live generator interface rather than assumed here.
In general, an Apache password-protection configuration can depend on information such as the resource being protected and the authentication details used by the server. However, this page does not claim that the Toolhox generator exposes each of these as a separate input. Use only the fields actually presented by the tool.
Do not enter passwords, usernames, directory paths, or other information into the generator unless you are comfortable with the page's stated data-handling practices. The supplied tool context does not establish whether submitted values are processed in the browser, transmitted to a server, or stored.
How to Use the HTACCESS Password Protection Generator
- Step 1: Open the HTACCESS Password Protection Generator and review the fields and options shown by the current tool interface.
- Step 2: Enter the requested configuration information using values appropriate for the website or directory you want to protect.
- Step 3: Review every generated directive before using it, especially authentication details and file or directory references.
- Step 4: Copy the generated
.htaccessconfiguration in the format provided by the tool. - Step 5: Place the configuration in the appropriate location on an Apache-compatible server, following your hosting provider's instructions.
- Step 6: Test the protected resource and confirm that authorized and unauthorized access behave as expected.
Technical Explanation
This is a generator, not a calculator. Its primary job is to turn user-provided configuration information into Apache .htaccess password-protection directives. There is therefore no single mathematical formula or unit conversion to document.
Apache password protection generally relies on HTTP authentication directives. A typical setup can use an authentication type, a protected-resource name, a password-file reference, and access requirements. The exact directives and values depend on the Apache configuration and the authentication method being used.
The important point is that the generated text is configuration code. Small changes to directive names, paths, file locations, or authentication settings can change how access control works. A configuration that is syntactically valid may still fail if the server does not support the required directive or if a referenced password file is missing or incorrectly configured.
Understanding the Output
The generated result should be treated as Apache configuration text rather than ordinary website copy. Review the output carefully before deployment. Look for references to files, directories, authentication settings, and access requirements.
| Output characteristic | What it means |
|---|---|
.htaccess configuration |
Text intended for an Apache directory configuration file. |
| Authentication directives | Rules that can control access to protected content. |
| File or path references | Values that may need to match the actual server environment. |
Example of the Expected Workflow
Suppose a site owner wants to restrict access to a website area used for private development work. The user would open the generator, enter the information requested by its interface, generate the configuration, inspect the resulting directives, and then deploy the configuration according to the Apache hosting environment.
This example explains the workflow only. It does not assume particular Toolhox fields or reproduce a specific generated configuration because the supplied tool context does not provide the generator's exact interface or output template.
Why Review the Generated Configuration?
Generated server configuration should always be checked before it is applied to a live site. The correct syntax depends on the server software, enabled modules, hosting setup, file locations, and other configuration details.
A common mistake is assuming that creating an .htaccess file automatically guarantees password protection. The server must support the required directives, and referenced authentication resources must be correctly configured. A wrong path or unsupported directive can prevent the expected protection from working.
It is also important to distinguish access protection from broader website security. An .htaccess authentication rule is one access-control mechanism. It does not by itself secure an entire website, remove application vulnerabilities, or replace appropriate server and application security practices.
Why Use This HTACCESS Password Protection Generator & How Our Generator Beats the Competition
The practical value of a generator is that it provides configuration text for a specific task without requiring the user to manually assemble every directive. The following comparison focuses on general methods rather than unsupported claims about specific competing products.
| Method | Ease of Use | Configuration Work | Best For | Limitations |
|---|---|---|---|---|
| Toolhox HTACCESS Password Protection Generator | Uses a dedicated generator interface | Generates configuration text from supplied inputs | Creating a starting point for Apache password protection | Exact behavior and supported options depend on the tool interface and server environment |
| Manual configuration | Requires knowledge of Apache directives | User writes and checks the configuration | Users who need full manual control | Syntax and configuration mistakes are possible |
| Spreadsheet or text template | Depends on the template | User edits predefined values or configuration text | Repeated configurations with a known template | Templates may not match every server environment |
| Professional server configuration software | Varies by software | May provide broader server-management features | Complex server administration | May be more than needed for a simple password-protection configuration |
The key practical advantage of using a dedicated generator is the focused workflow: provide the information requested by the tool and receive configuration text that can then be reviewed. It should not be understood as a guarantee that the output is suitable for every Apache installation.
Assumptions and Limitations
- The tool is intended for generating Apache
.htaccesspassword-protection configuration. - The supplied context does not document the exact input fields, optional settings, or output template.
- The tool's exact internal implementation is not provided.
- The generated configuration may require adjustment for a particular hosting environment.
- Apache and hosting-provider support for the relevant directives should be confirmed before deployment.
- File paths and authentication resources must be correctly configured on the server.
- A generated configuration should be reviewed and tested before being used on a live website.
- The supplied information does not document how entered data is processed or stored.
- Users should avoid entering sensitive information unless the page clearly explains its data-handling practices.
When Should You Get Additional Technical Help?
Consider additional technical review when the protected content is business-critical, when the server uses a custom Apache configuration, when authentication must meet a specific organizational requirement, or when access control must be integrated with a larger application security system. A server administrator or developer can verify that the generated directives match the actual environment.
For routine testing, the most useful approach is to generate the configuration, inspect it, apply it in the correct Apache location, and test access from an unauthorized session as well as an authorized one. Keep a known-good configuration or backup available so that an incorrect server rule can be reversed if needed.